Jigsaw
- 84
- Global rank
- 68
- Month rank
- 59
- Week rank
The Jigsaw ransomware, initially detected in 2016, encrypts files on compromised systems and requires a ransom payment in Bitcoin. If the ransom is not paid, the malware starts deleting files, increasing the pressure on victims to comply. Its source code is publicly accessible, allowing various threat actors to customize and repurpose the malware for different objectives.
- Ransomware
- Type
- Unknown
- Origin
- 1 March, 2016
- First seen
- 19 October, 2026
- Last seen
How to analyze Jigsaw with ANY.RUN
IOCs
IP addresses
- 20.165.94.63
- 74.178.240.51
- 131.253.33.203
- 23.59.18.102
- 40.126.31.69
- 23.52.181.141
- 150.171.109.71
- 172.217.118.4
- 2.16.204.141
- 172.211.123.248
- 142.251.127.84
- 48.209.138.168
- 142.251.157.119
- 142.251.13.101
- 48.192.1.64
- 192.178.183.94
- 92.123.104.28
- 20.190.160.130
- 52.110.17.68
- 142.251.13.113
Hashes
- 3ae96f73d805e1d3995253db4d910300d8442ea603737a1428b613061e7f61e7
- 619e246fc0ac11320ff9e322a979948d949494b0c18217f4d794e1b398818880
- 2501fe92ddbf8d2ae4b05d348504d090268c0e7397188856f38e4e72c5d4e918
- afa757edcdd80c7900ab043375219eb22a0a4b088d5d084dda9dcaedc1014d0e
- d5c378306d86b898e874d79f2b63ac6af1b9a2a628b867630dc71b76d6726625
- 979fb070cd41eb955391fd9e10a3e272fd7449ee4f462c3afe3bb622f1e6af8b
- e3940c668de8d0c6af7c438fca01db65b3a1caea4eab343fc3cf8ae53502efe3
- 1c79647381f072d4c268e4c4ae60e6207390c2cd3d3a4176b30888b501616162
- 23dd9e7e829c72f8ed99ad0312c7625c57d4b590a32c3fb7c5daf3d460f305ab
- 808d8df9e11c4848bdfeef18c6c36730368a94b9955fe0bfda7ad8e346365295
- 717770f3195c40f561b3d6ec873463dd4e2a3fda53f64f3dd8937a353d6cda91
- 644cb6c57161820b56ad7ea640f1354ff751cf1bc5290aede33da19daf065c81
- 754f334b19cc5c75f9bc28bc33529449d95fc97034b7841daf1be896510a5ed2
- 3e489ab55f211c5a19ccc8b680aa9d2d1fbd5018ac5d5da9a6bb68247db90d3e
- 62ee36829210619f16fc85286735e7a235721662fc207be109e8f13a5895d0f3
- dc1fb62706fc445511120b73f497d4a2da9306f6947b7a53840b66a84c62e62c
- 0746432cfef82195e36676f86e431188f1b70970913c2d5bbfe8192630430d92
- 36a9e7f1c95b82ffb99743e0c5c4ce95d83c9a430aac59f84ef3cbfab6145068
- 5a99501fd3a5e3a41dd6e86fe5d32521d974c218c9d718c364e36d37fcd1048b
- e6bc40d9d09c8090f941b2786ab9a72f160093c1bfd7337c3a844c540269513a
Domains
- slscr.update.microsoft.com
- officeclient.microsoft.com
- accounts.google.com
- activation-v2.sls.microsoft.com
- crl.microsoft.com
- www.microsoft.com
- www.bing.com
- ocsp.digicert.com
- clients2.google.com
- fe3cr.delivery.mp.microsoft.com
- www.gstatic.com
- update.googleapis.com
- client.wns.windows.com
- safebrowsingohttpgateway.googleapis.com
- settings-win.data.microsoft.com
- go.microsoft.com
- self.events.data.microsoft.com
- www.google.com
- google.com
- ecs.office.com
URLs
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
- https://www.bing.com/dsb/search?dsbmr=1&format=dsbjson&client=windowsminiserp&dsbschemaversion=1.1&dsbminiserp=1&q=q&cc=us&setlang=en-us&clientdatetime=10%2f19%2f2026%2c%2010%3a47%3a49%20am
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- https://www.bing.com/dsb/scenario?name=trendingsearchwithcache&cc=us&setlang=en-us
- https://www.bing.com/threshold/xls.aspx?t=5&dl=1&f=9&wsbc=1
- https://officeclient.microsoft.com/config16/?syslcid=1033&build=16.0.16026&crev=3
- https://ecs.office.com/config/v2/office/officeclicktorun/16.0.16026.20140/production/cc?&clientid=%7b48ba7fdf-353c-4fe5-8d8f-9e31911a3891%7d&application=officeclicktorun&platform=win32&version=16.0.16026.20140&msoversion=16.0.16026.20140&processname=officeclicktorun.exe&audience=production&build=ship&architecture=x64&osversion=10.0&osbuild=19045&channel=cc&installtype=c2r&sessionid=%7b0ff3aca0-6040-430a-8ff3-e4f1534fd0e6%7d&labmachine=false
- https://go.microsoft.com/fwlink/?linkid=2257403&clcid=0x409
- http://clients2.google.com/time/1/current?cup2key=8:s6x7ijvprzjbrukt5kcyppkhw8f98pcbahgg0vo8cxm&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
Last seen at
What is Jigsaw Malware?
Jigsaw ransomware, initially detected in 2016, is a form of malware designed to encrypt files on a victim's system and extort a ransom payment in Bitcoin to restore access.
The creators of Jigsaw incorporate themes and visuals from the horror movie Saw, utilizing threatening messages inspired by the film to pressure victims into complying with the ransom demands.
If the victim does not pay the ransom, Jigsaw begins deleting files from the infected system, increasing the urgency for victims to act. This approach not only encrypts valuable data but also introduces a time-sensitive element that can cause significant distress and data loss.
The original malware is no longer active, as researchers were able to quickly develop decryption tools. However, Jigsaw's source code is openly available, allowing different threat actors to modify and adapt the malware for various purposes, including data theft.
Jigsaw Malware Technical Details
Jigsaw has a range of capabilities which vary across different variants.
- The original Jigsaw used the AES encryption algorithm to lock files, making them inaccessible without the decryption key.
- The malware employed over 80 different file extensions for encrypted files, including the .FUN, complicating the identification and recovery process.
- It displayed ransom notes with instructions for payment, typically demanding Bitcoin in exchange for decryption.
- Jigsaw verified ransom payments by querying a Bitcoin wallet address via HTTP requests. Upon detecting the required funds, it initiates the decryption process.
- Despite the development of decryption tools by researchers, Jigsaw continues to evolve, with new variants emerging that incorporate additional malicious functionalities.
Jigsaw Execution Process
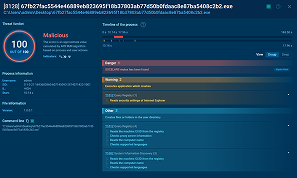
To analyze any sample of Jigsaw, you can upload it to ANY.RUN’s Interactive Sandbox, a safe cloud environment for examining malicious URLs and files. Check out this analysis of a Jigsaw sample
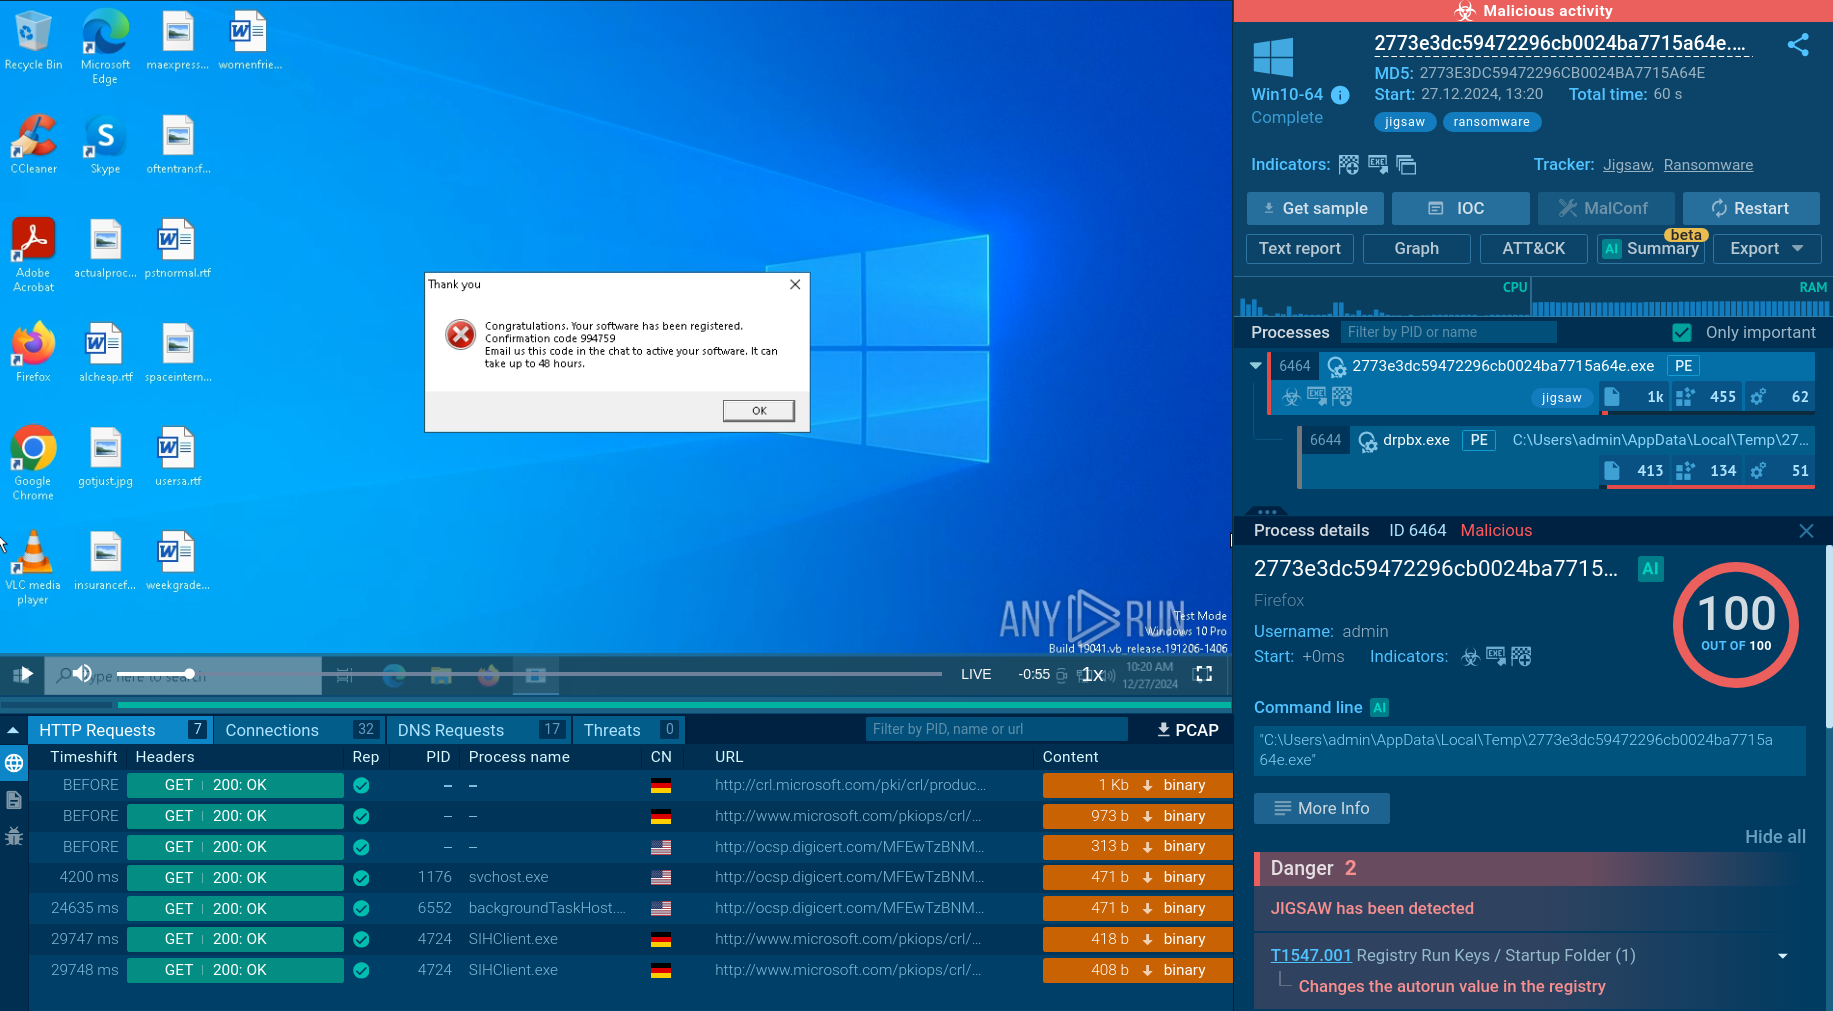
The execution process of Jigsaw ransomware involves several critical steps to ensure the encryption of files and the extortion of victims. Upon infecting a system, the malware begins by encrypting the files and displaying a ransom note with payment instructions. The ransom note typically includes a countdown timer, indicating the time remaining before files start being deleted.
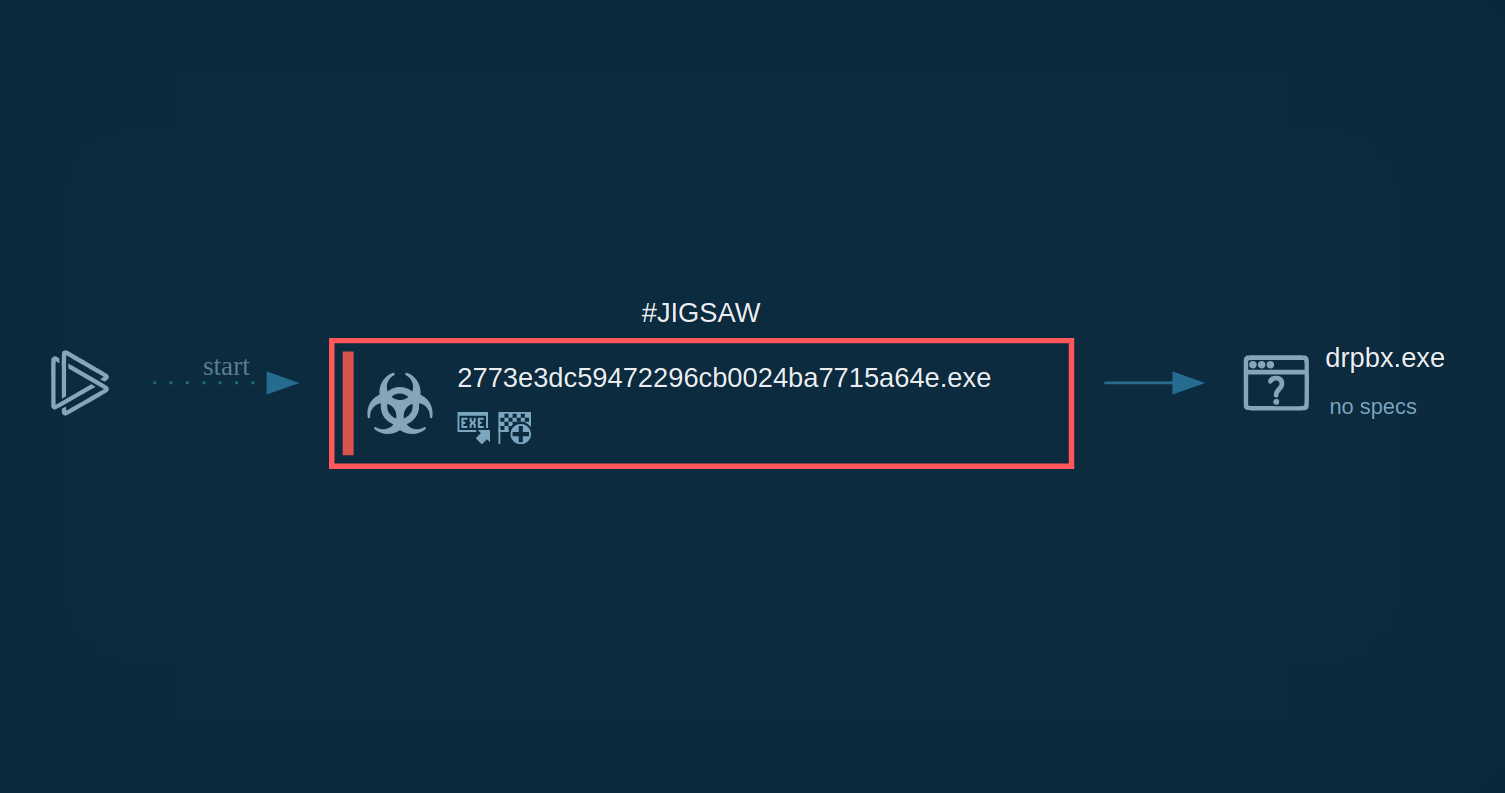
To verify that the ransom has been paid, Jigsaw queries a Bitcoin wallet address via HTTP requests. If the malware detects that the required funds have been deposited, it triggers the decryption process, restoring access to the encrypted files.
Jigsaw Distribution Methods
The distribution methods for Jigsaw ransomware have evolved significantly since its inception. Initially, the malware was spread through fake software executables that mimicked legitimate programs. These executables were designed to trick users into downloading and running the malicious files, leading to infection.
However, newer variants of Jigsaw utilize a broader range of distribution channels. Some of the most common methods include:
- Phishing Emails: Threat actors send phishing emails with malicious attachments or links that, when opened, download and execute the Jigsaw ransomware.
- File-Sharing Platforms: Malicious files are hosted on file-sharing platforms, where unsuspecting users may download them, leading to infection.
- Compromised Websites: Jigsaw may be bundled with other malware as a downloader from compromised websites. Visitors to these sites may unknowingly download and install the ransomware.
Each threat actor may utilize their own channel of distribution, making it challenging to predict and defend against the spread of Jigsaw ransomware.
Collect Threat Intelligence on Jigsaw Ransomware
To gather information about Jigsaw ransomware and collect relevant intelligence, utilize Threat Intelligence Lookup.
This service provides access to a comprehensive database containing insights from millions of malware analysis sessions conducted in the ANY.RUN sandbox. With over 40 search parameters, users can find specific data related to threats, including IP addresses, domains, file names, and process artifacts.
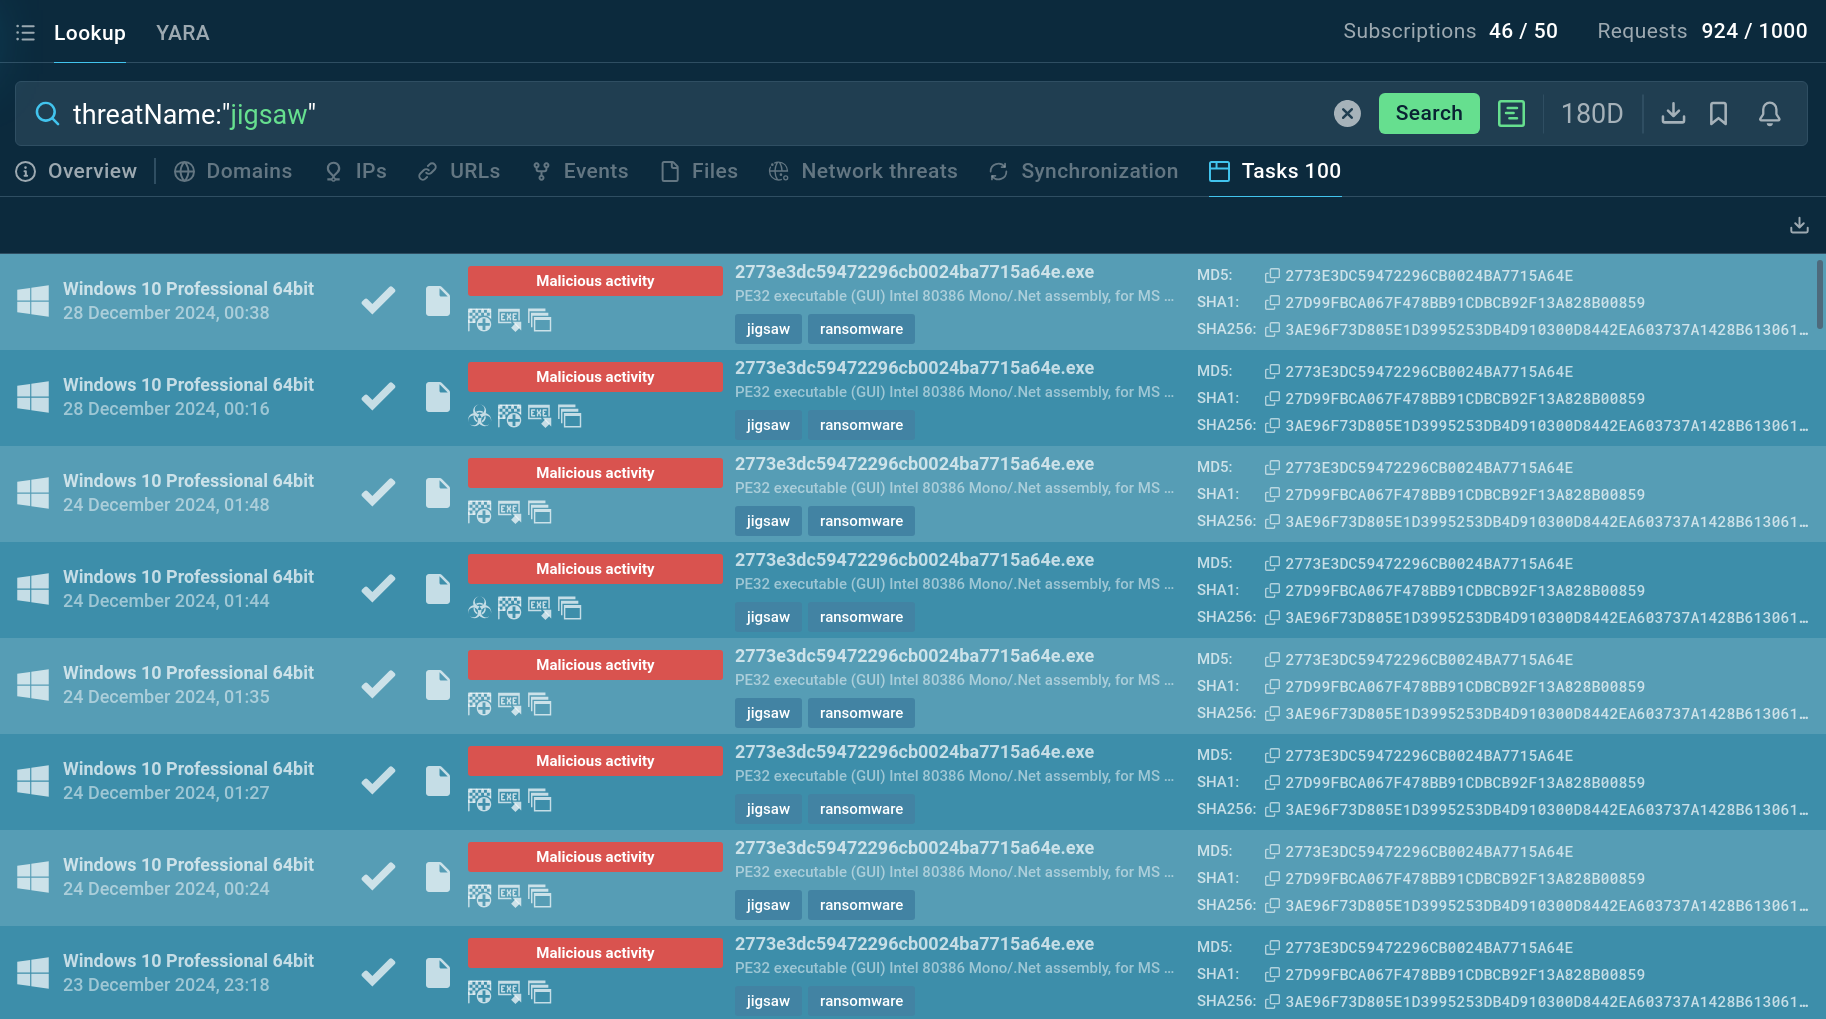
For example, you can search for Jigsaw by its name or related artifacts. A query like threatName:"Jigsaw" will retrieve all associated samples and sandbox results relevant to this ransomware. This tool is invaluable for staying informed about the latest variants and indicators of Jigsaw, helping security professionals to better understand and mitigate the threat.
Conclusion
Although the Jigsaw ransomware no longer presents a significant threat in the cybersecurity landscape, as it did in 2016, access to its source code makes it a potential security risk to organizations. To prevent possible infections with Jigsaw, it is important to implement comprehensive security measures, including proactive sandbox analysis.
Use ANY.RUN’s Interactive Sandbox to quickly examine suspicious files and URLs to identify threats early and address them before they have a chance to compromise your infrastructure.
Sign up for a free ANY.RUN account to access unlimited analysis!
Other malware & phishing threats
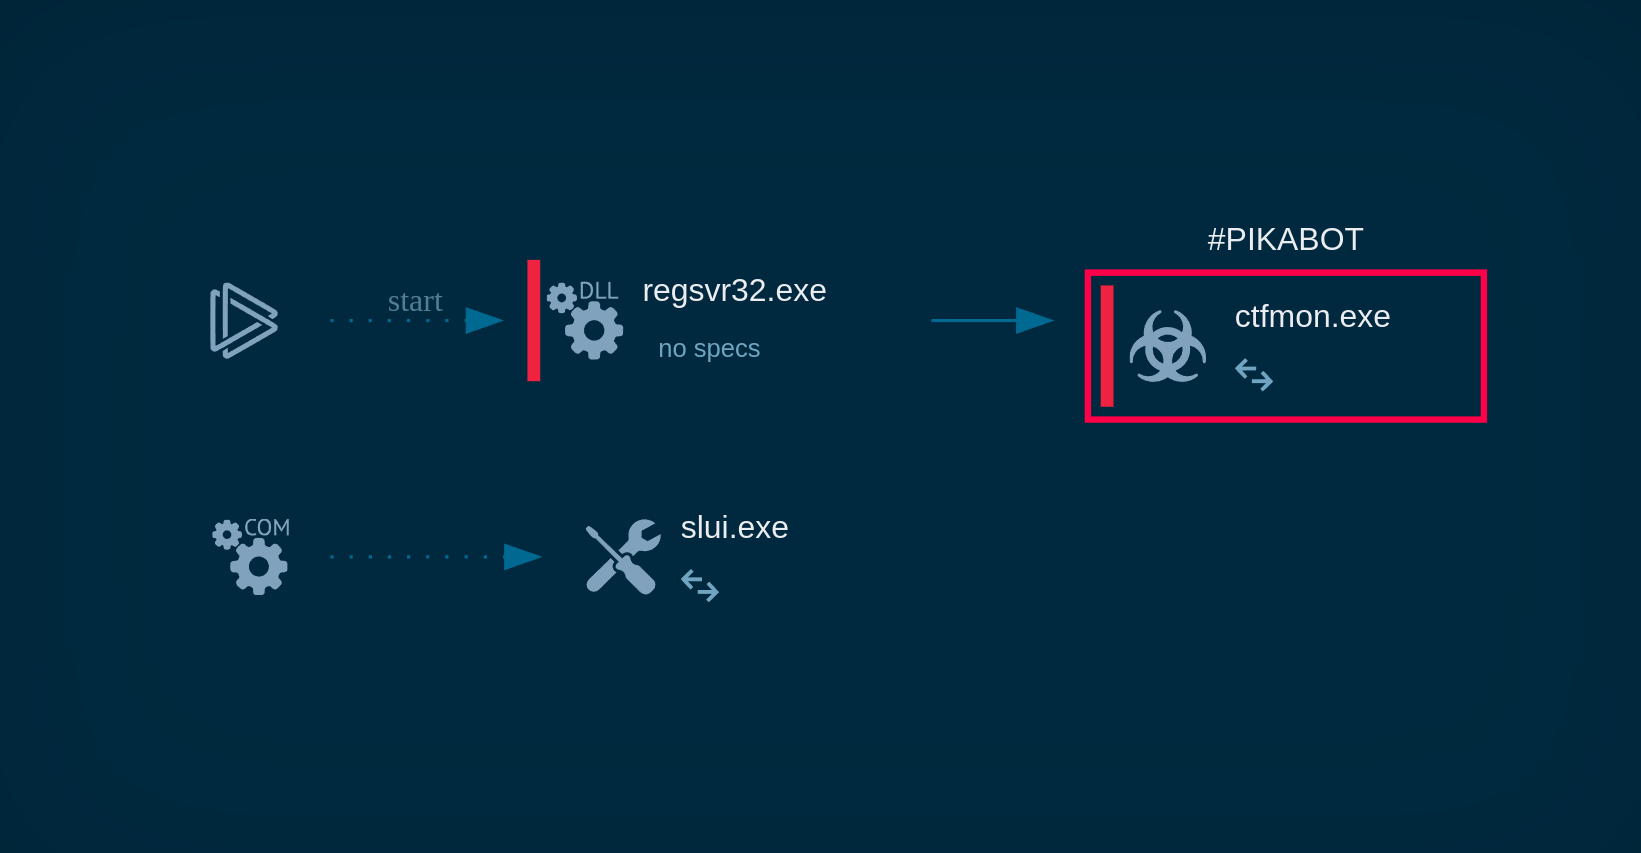 PikabotPikabot is a trojan malware with a focus on loader capabilities. Pikabot is also used for other activities, such as executing commands on the infected system. The earlier versions of the malware made use of extensive code obfuscation to evade detection. Upon infection, it collects system information and sends it to command-and-control servers.
 DCRatDCrat, also known as Dark Crystal RAT, is a remote access trojan (RAT), which was first introduced in 2018. It is a modular malware that can be customized to perform different tasks.
For instance, it can steal passwords, crypto wallet information, hijack Telegram and Steam accounts, and more. Attackers may use a variety of methods to distribute DCrat, but phishing email campaigns are the most common.
 PonyPony is a malware with two main functions — stealing information and dropping other viruses with different tasks on infected machines. It has been around since 2011, and it still actively attacks users in Europe and America.
 GandCrabGandCrab is probably one of the most famous Ransomware. A Ransomware is a malware that asks the victim to pay money in order to restore access to encrypted files. If the user does not cooperate the files are forever lost.
 Pulsar RATPulsar RAT is a derivative of Quasar RAT with extensive functionality including keylogging, cryptocurrency wallet clipping, credential theft, file management, remote shell execution, and data exfiltration capabilities. As a modular, open-source remote administration tool designed for Windows systems, Pulsar introduces significant enhancements over its predecessor.
 SocelarsSocelars is an information-stealing Trojan (often categorized as spyware/stealer) that focuses on collecting sensitive data from Windows systems, with standout reporting around Facebook Ads Manager and session cookie theft.
Unlike “noisy” malware that immediately breaks something, Socelars quietly converts a single infected machine into access: logged-in sessions, business account data, and pathways to monetization.