StrelaStealer
- 141
- Global rank
- 180
- Month rank
- 166
- Week rank
StrelaStealer is a malware that targets email clients to steal login credentials, sending them back to the attacker’s command-and-control server. Since its emergence in 2022, it has been involved in numerous large-scale email campaigns, primarily affecting organizations in the EU and U.S. The malware’s tactics continue to evolve, with attackers frequently changing attachment file formats and updating the DLL payload to evade detection.
- Stealer
- Type
- Unknown
- Origin
- 1 November, 2022
- First seen
- 13 June, 2026
- Last seen
How to analyze StrelaStealer with ANY.RUN
IOCs
IP addresses
- 48.209.138.189
- 48.209.133.15
- 23.11.41.157
- 204.79.197.203
- 48.192.1.64
- 135.232.92.97
- 135.232.92.137
- 48.209.6.48
- 23.48.23.143
- 23.52.181.212
- 172.211.123.248
- 92.123.104.30
- 40.126.31.131
- 88.221.169.152
- 135.233.95.144
- 74.178.240.51
- 172.211.123.250
- 48.209.138.168
- 184.86.251.15
- 20.190.159.130
Hashes
- 2d369650bb2ce59752cbd5014be32a918548e52a318149268f448fcd46db0a62
- f38cd6aa26981ba1eea4fb0ec8f9db212e518f65f28556e108ef74d92e4809b6
- 5ff517a97b05c9ca005f75dc7b207c05db3b57a996cde03dd5af33452c84c88d
- 8e191c20eecc707fc6ce933eed7a4360b5bf5c5edfa87f7123103d625eeecd97
- f2caaf774ab4ac5e7b5d9299117eb1bad22e025a2e530ffc29496456760390b6
- 4b0fb440200468c36ed851ded27258b59b6be524482ea37b9a745ac97ec615cd
- c52c62a7c50daf7d3f73ec16977cd4b0ea401710807d5dbe3850941dd1b73a70
- d571ef33b0e707571f10bb37b99a607d6f43afe33f53d15b4395b16ef3fda665
- 0dd48f2745ae310bfee24d2de1dea6c2c4dcfa890a8b64985bdf5ef6685a58c7
- a8a79d350c2a5e3bc36226633a8e0bed0dfab184e77f38fc8f0820ebacf8eafc
- fb077c966296d02d50ccbf7f761d2a3311a206a784a7496f331c2b0d6ad205c8
- 8223a912160354e05735522fdb339dc59b353ad5d1e4f4cfa94898dc348e748f
- 8c5fa4b29519d17593e923bc6a9a284df7a6d07fac42f897110b8fb2e0baeef5
- af0edb67c2219b803c3eb6c1dee6f2d41a3fe00468a9da8be8ef5056d701abf3
- 97a4755fe9e653a08969f1933e3db19c712078b227bd5aa6799093abc5a0edc3
- c2784e33158a807135850f7125a7eaabe472b3cfc7afb82c74f02da69ea250fe
- 137461792537a2e56a6475e81e2b9ad7a2bdabf1f4738fae186dca3022357349
- 5487ee44a4cd706d0086522e90c59c76cdf2ac68ce506fd3eae6054b9220c0cf
- d673805547a0228d2f57a5ad551b8760cfcc521f38c49284ed3976e3515bca49
- 89d98eff14e2cf1c2314efdf392339e62d7e786f100202a7377bf7b22095a0c5
Domains
- ocsp.digicert.com
- fe3cr.delivery.mp.microsoft.com
- client.wns.windows.com
- activation-v2.sls.microsoft.com
- settings-win.data.microsoft.com
- www.microsoft.com
- crl.microsoft.com
- slscr.update.microsoft.com
- oneocsp.microsoft.com
- google.com
- wet-envelope-beam-laser.trycloudflare.com
- www.bing.com
- login.live.com
- self.events.data.microsoft.com
- aus5.mozilla.org
- recaptcha.net
- play.google.com
- safebrowsingohttpgateway.googleapis.com
- tracking.prf.hn
- push.services.mozilla.com
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaagb6jmmcovb6saaaaaaay%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=1&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- http://www.microsoft.com/pkiops/crl/micsecserca2011_2011-10-18.crl
- https://settings-win.data.microsoft.com/settings/v3.0/onesettings/client?osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&localdeviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&attrdataver=186&osuilocale=en-us&osskuid=48&app=wosc&appver=&isflightingenabled=0&telemetrylevel=1&devicefamily=windows.desktop
- https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/muse?processorclockspeed=3094&flightids=&updateoffereddays=4294967295&branchreadinesslevel=cb&oemmanufacturername=dell&isclouddomainjoined=0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&sku=48&activationchannel=retail&attrdataver=186&ismdmenrolled=0&processorcores=6&processormodel=amd%20ryzen%205%203500%206-core%20processor&totalphysicalram=6144&primarydisktype=4294967295&flightingbranchname=&chassistypeid=1&oemmodelnumber=dell&systemvolumetotalcapacity=260281&sampleid=95271487&deviceclass=windows.desktop&app=muse&disabledualscan=0&appver=10.0&oemsubmodel=j5cr&locale=en-us&isalwaysonalwaysconnectedcapable=0&ms=0&defaultuserregion=244&updateserviceurl=http%3a%2f%2fneverupdatewindows10.com&osver=10.0.19045.4046.amd64fre.vb_release.191206-1406&os=windows&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&deferqualityupdateperiodindays=0&ring=retail&deferfeatureupdateperiodindays=30
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20product%20root%20certificate%20authority%202018.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://login.live.com/rst2.srf
- https://login.live.com/ppsecure/deviceaddcredential.srf
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/updatehealthtools?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=s:bad99146-31d3-4ec6-a1a4-be76f32ba5d4&sampleid=s:95271487&appver=10.0.19041.3626&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=sedimentpack&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://influence-meets-town-came.trycloudflare.com/gun/TheDll.wsf
- https://influence-meets-town-came.trycloudflare.com/gun/theDll.js
Last seen at
What is StrelaStealer malware?
StrelaStealer is an information-stealing malware first observed in late 2022, primarily targeting login credentials from popular email clients. This malware is known for its large-scale phishing campaigns, particularly across Europe and the United States, where it has successfully compromised numerous organizations.
The malware is predominantly distributed through phishing emails containing malicious attachments, such as ZIP files or ISO files, which execute the payload once opened.
StrelaStealer employs various obfuscation and anti-analysis techniques to evade detection, including control flow obfuscation and removing PDB strings, making it increasingly difficult for security tools to detect and analyze.
StrelaStealer malware technical details
StrelaStealer’s primary function is to steal email login information, which is then transmitted back to the attacker’s command-and-control (C2) server.
This stolen data can be used to conduct further malicious activities, such as sending spam emails, launching spear-phishing attacks, or exfiltrating sensitive information.
Although it is not explicitly marketed as Malware-as-a-Service (MaaS), the ongoing development and frequent updates suggest that it is actively maintained and potentially distributed through cybercriminal networks.
The primary capabilities of the StrelaStealer malware include:
- Stealing login credentials from popular email clients, capturing usernames and passwords.
- Transmitting stolen email login data to the attacker’s command-and-control (C2) server.
- Distributing itself through large-scale phishing campaigns, often targeting organizations in the EU and U.S.
- Using advanced obfuscation methods, such as control flow obfuscation, to evade detection and hinder analysis.
- Utilizing compromised email accounts to send out further phishing emails, perpetuating the attack cycle.
- Adapting its payload delivery methods, changing file formats and attachment types to avoid detection by static security measures.
- Ensuring it remains active on infected systems through various persistence techniques, making removal difficult.
StrelaStealer execution process
To see how StrelaStealer operates, let’s launch an analysis session using its sample in the ANY.RUN sandbox.
As noted, StrelaStealer is primarily distributed through phishing emails that often contain ZIP file attachments. These emails typically use localized language and subject lines resembling invoices or bills (e.g., "Factura/Rechnung/Invoice###/PO###") to lure victims into opening them. When a victim opens the ZIP file, it contains a JScript file that, upon execution, may drop a base64-encoded file and a batch file onto the system.
The batch file utilizes the certutil -f decode command to decode the base64 file, which creates a Portable Executable (PE) DLL file. The DLL file is then executed using the rundll32.exe or regsvr32.exe process, specifically calling an exported function (often named "hello" in the latest variants) to initiate the malware's operations.
In our sample, the command line contains "davwwwroot" in the path to the downloaded DLL file.
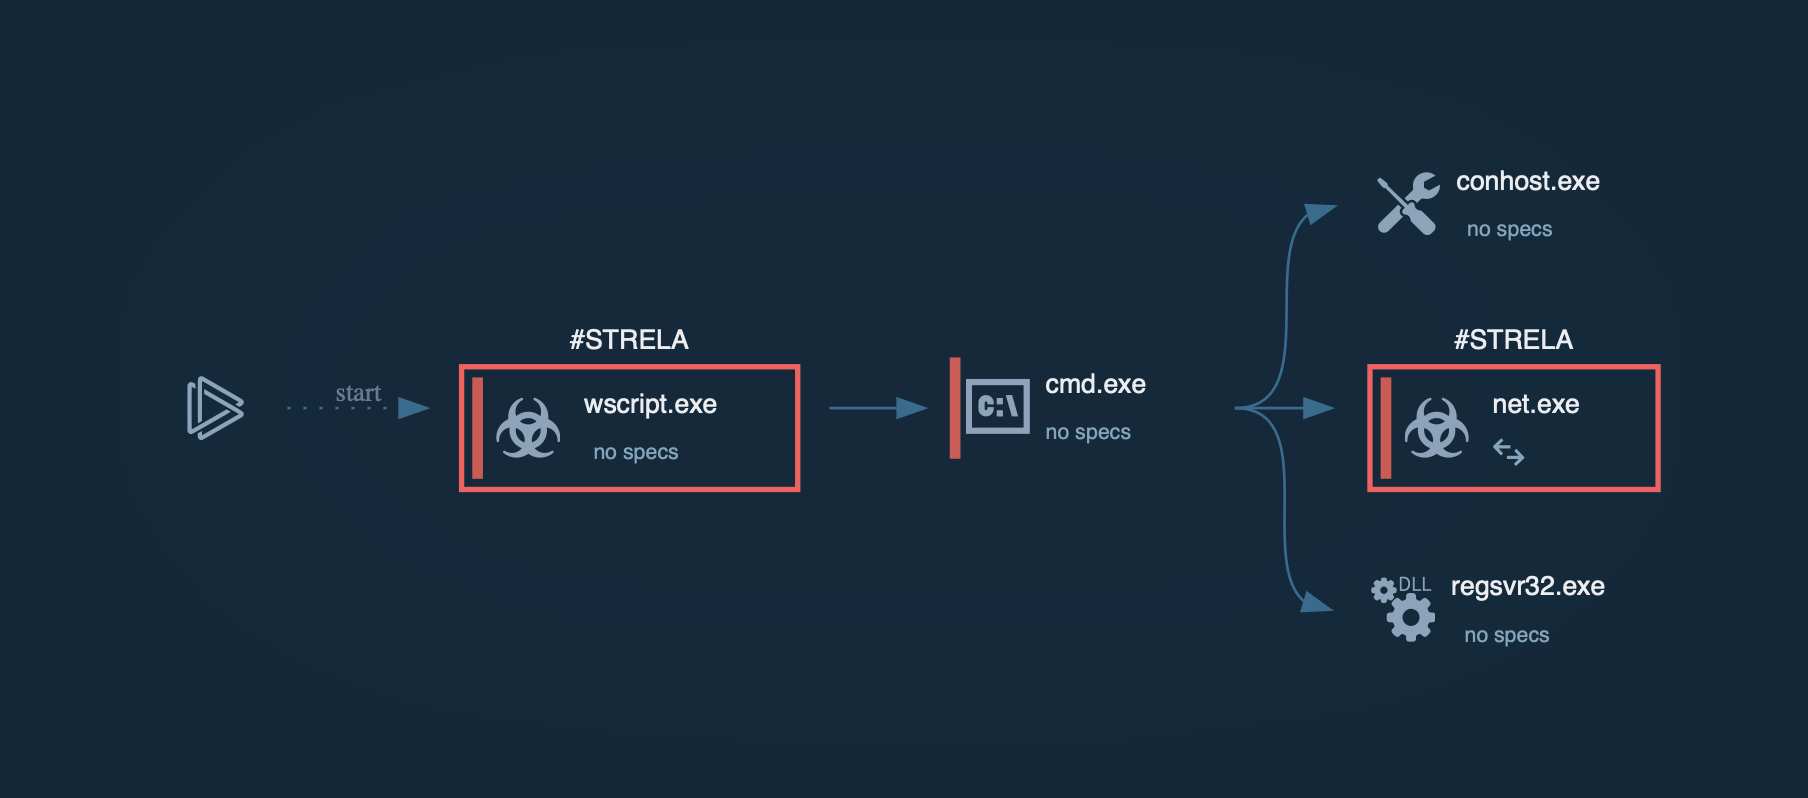
Once executed, StrelaStealer is designed to steal email login credentials from popular email clients such as Outlook and Thunderbird. The stolen credentials are then sent back to the attacker's Command and Control (C2) server for further exploitation.
The latest variants of StrelaStealer employ advanced obfuscation techniques, including control flow obfuscation and the removal of debugging symbols (PDB strings), making it more challenging for security analysts to detect and analyze the malware. The malware's code includes excessively long arithmetic instructions to complicate execution in sandbox environments, potentially causing timeouts during analysis.
Since its emergence in 2022, StrelaStealer has targeted over 100 organizations across the U.S. and Europe, with significant campaigns observed in late 2023 and early 2024. The threat actors continue to adapt their strategies to evade detection while maximizing the impact of their attacks.
StrelaStealer malware distribution methods
StrelaStealer is primarily distributed through:
- Phishing emails: Emails with malicious attachments (e.g., ZIP or ISO files) or links that lead to malware downloads.
- Loaders: Initial malware that infects the system and then downloads StrelaStealer.
- Fake websites: Sites mimicking legitimate services, tricking users into downloading the malware.
Conclusion
StrelaStealer is a dangerous malware due to its ability to steal email credentials, evade detection through advanced obfuscation techniques, and spread rapidly via phishing campaigns. Its ongoing development and adaptability make it a persistent threat to organizations.
ANY.RUN is a cloud-based interactive malware analysis platform that enables users to safely analyze and observe the behavior of malicious files in a secure environment. It provides real-time insights, helping security professionals collect indicators of compromise (IOCs) and understand the tactics used by malware like StrelaStealer, ultimately strengthening defenses against such threats.
Sign up for a free ANY.RUN account today and take your cybersecurity to the next level.
Other malware & phishing threats
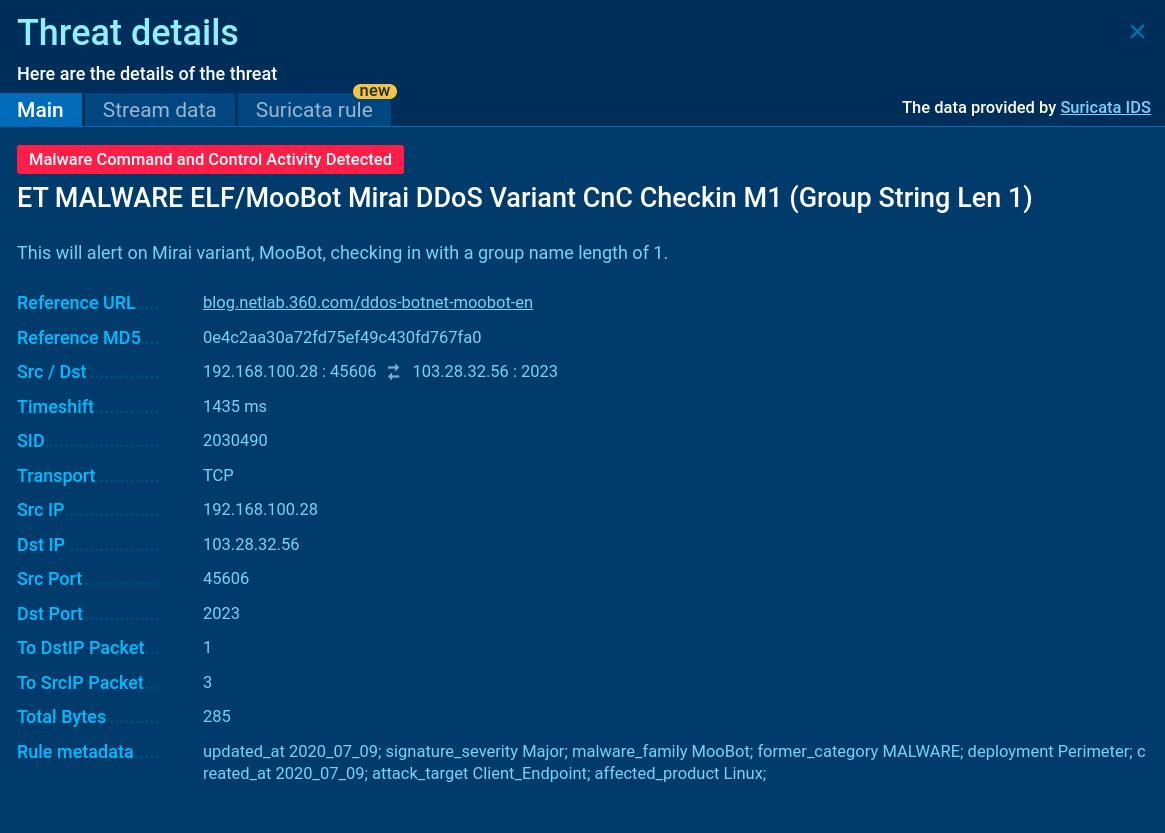 MiraiMirai is a self-propagating malware that scans the internet for vulnerable IoT devices and infects them to create a botnet. Mirai variants utilize lists of common default credentials to gain access to devices. Mirai's primary use is for launching distributed denial-of-service (DDoS) attacks, but it has also been used for cryptocurrency mining.
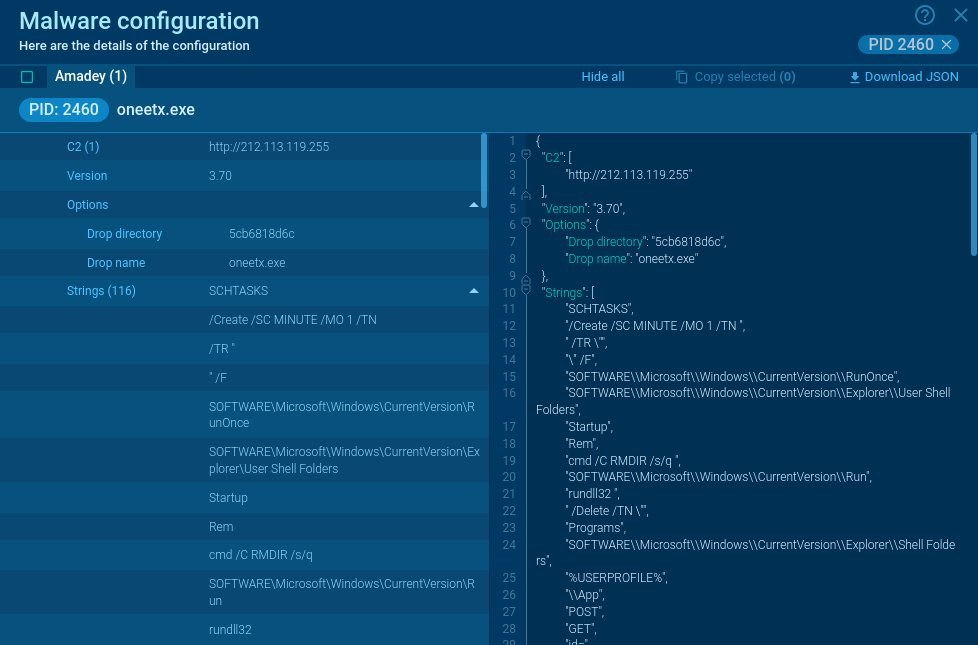 AmadeyAmadey is a formidable Windows infostealer threat, characterized by its persistence mechanisms, modular design, and ability to execute various malicious tasks.
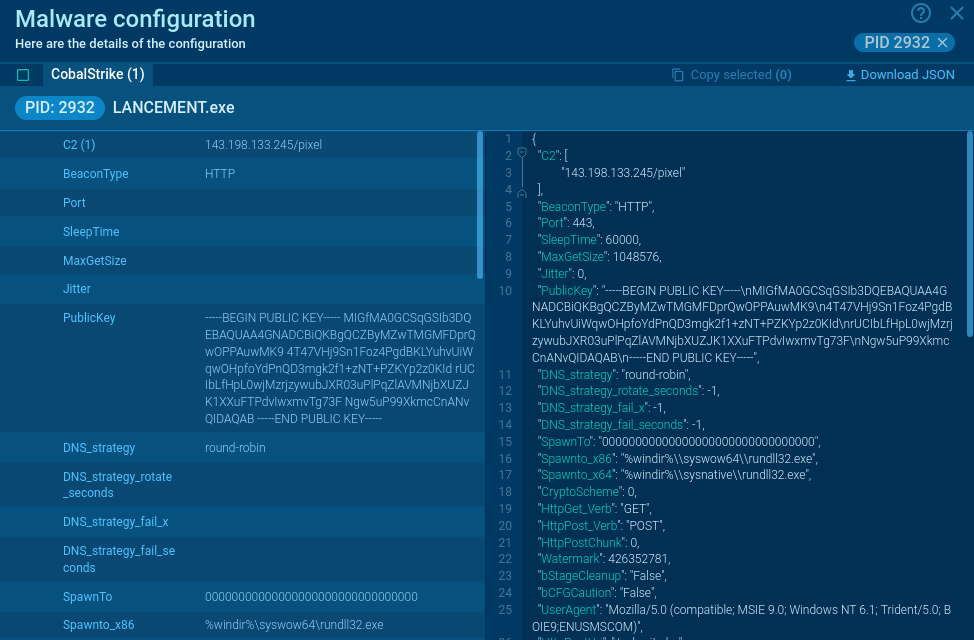 Cobalt StrikeCobalt Strike is a legitimate penetration software toolkit developed by Forta. But its cracked versions are widely adopted by bad actors, who use it as a C2 system of choice for targeted attacks.
 Neptune RATNeptune RAT is a Visual Basic .NET remote access trojan that gives attackers full control over infected Windows machines while stealing credentials from 270+ applications, hijacking cryptocurrency transactions, spying on victims in real time, and, in its most destructive mode, wiping the operating system entirely. Marketed openly on GitHub, Telegram, and YouTube as the "Most Advanced RAT," it is distributed under a malware-as-a-service model.
 BackdoorA backdoor is a type of cybersecurity threat that allows attackers to secretly compromise a system and conduct malicious activities, such as stealing data and modifying files. Backdoors can be difficult to detect, as they often use legitimate system applications to evade defense mechanisms. Threat actors often utilize special malware, such as PlugX, to establish backdoors on target devices.
 Gh0st RATGh0st RAT is a malware with advanced trojan functionality that enables attackers to establish full control over the victim’s system. The spying capabilities of Gh0st RAT made it a go-to tool for numerous criminal groups in high-profile attacks against government and corporate organizations. The most common vector of attack involving this malware begins with spam and phishing emails.